
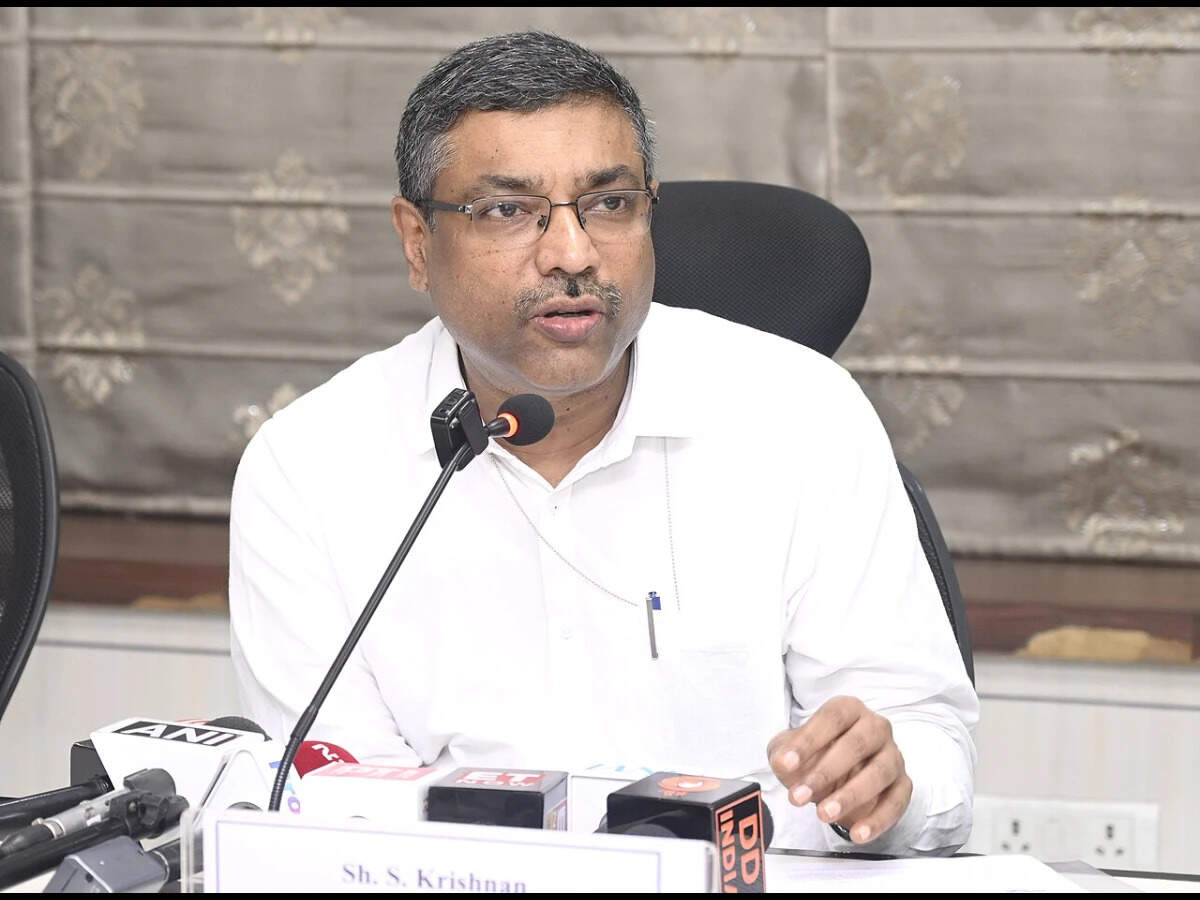
The Ministry of Electronics and Information Technology (MeitY) took another step towards implementing India’s digital data protection regime on November 14, 2026, when Secretary S. Krishnan launched the online portal for registering Consent Managers under the Digital Personal Data Protection (DPDP) Act, 2023. The registration framework came into effect a day earlier, allowing eligible Indian-incorporated companies with a minimum net worth of ₹2 crore to apply for registration with the Data Protection Board of India.The development introduces a regulated intermediary into India’s data governance architecture, intended to give individuals greater control over how organisations collect and process their personal information. Its significance lies not merely in establishing another compliance mechanism, but in addressing a persistent weakness in digital services: individuals frequently consent to the processing of their information without having an equally convenient mechanism to review or withdraw that permission.India’s expanding digital economy generates enormous volumes of personal information through banking, telecommunications, e-commerce, healthcare, education and government services. A single individual may interact with dozens of digital platforms, each maintaining separate consent records and privacy procedures. The Consent Manager framework seeks to address this fragmentation through interoperable platforms that allow individuals to manage permissions across participating organisations.Under the DPDP framework, registered Consent Managers will enable individuals, legally described as Data Principals, to give, review, manage and withdraw consent through accessible and transparent interfaces. Applications can be submitted through dpbi.gov.in, while the Data Protection Board will examine eligibility and publish the names of registered entities. Consent Managers must act on behalf of Data Principals and remain accountable to them, rather than functioning simply as compliance service providers for businesses.
The distinction between obtaining consent and managing consent is fundamental to effective data protection. A company may obtain permission when a customer registers for a service, but meaningful control requires that the customer can subsequently identify the permission, understand its purpose and withdraw it without unnecessary difficulty. Consent that cannot be conveniently reviewed or withdrawn offers limited practical protection, even when the original authorisation satisfies formal legal requirements.India’s DPDP Act emerged from a prolonged constitutional and legislative debate over privacy, technological innovation and institutional accountability. In August 2017, the Supreme Court, in Justice K.S. Puttaswamy (Retd.) v. Union of India, unanimously recognised privacy as a fundamental right under the Constitution. Parliament subsequently enacted the DPDP Act in August 2023, establishing a statutory framework for processing digital personal data. The DPDP Rules, notified in November 2025, provided the operational architecture for implementing the legislation in phases.The legislation distinguishes between Data Principals, whose personal information is processed, and Data Fiduciaries, which determine the purposes and means of processing. It establishes obligations concerning lawful processing, transparency, security safeguards and individual rights, subject to specified exceptions. The Act also provides for substantial financial penalties, including penalties of up to ₹250 crore for failures to implement reasonable security safeguards against personal data breaches.The Consent Manager framework is integral to this architecture because statutory rights require practical mechanisms through which individuals can exercise them. Without an accessible system for managing permissions, informed consent risks becoming little more than a procedural requirement. Interoperability is especially important: individuals should not have to navigate numerous complicated systems simply to determine which organisations possess permission to process their information. Consent Managers can facilitate this process, although they do not replace the legal responsibilities of Data Fiduciaries.The framework nevertheless presents substantial regulatory and operational challenges. The DPDP Rules prescribe eligibility conditions, technical safeguards, governance requirements and restrictions intended to prevent conflicts of interest. Consent Managers must maintain appropriate records and operate without gaining access to the personal data whose processing permissions they facilitate. These safeguards are essential because an intermediary managing consent across multiple organisations could itself become a source of privacy risk if its operations are inadequately supervised.The ₹2 crore minimum net-worth requirement establishes a financial eligibility threshold, but capital adequacy alone cannot guarantee technical competence, institutional independence or effective cybersecurity. The Data Protection Board will have to evaluate applicants against these requirements and ensure continuing compliance after registration. The regulatory architecture must also accommodate innovative technology companies without compromising the security and reliability expected of entities entrusted with managing sensitive consent-related information.Another challenge concerns public adoption. Consent-management platforms will succeed only if individuals understand their purpose and find them convenient to use. Multilingual interfaces, accessibility features, transparent procedures and straightforward withdrawal mechanisms will be particularly important in a country with substantial differences in digital literacy. Businesses must also integrate their systems with registered intermediaries without compromising security or creating disproportionate compliance costs.The framework must also be understood within the limitations of consent-based regulation. Not every instance of personal data processing under the DPDP Act depends on consent; the legislation permits certain processing for specified legitimate uses. Moreover, withdrawing consent does not automatically eliminate every legal basis for retaining information. Consent Managers must therefore communicate clearly what withdrawal achieves, what obligations remain with Data Fiduciaries and when other statutory provisions apply.The next major implementation milestone is May 13, 2027, when important provisions governing individual rights, Data Fiduciary obligations and regulatory enforcement are scheduled to become operational. The intervening period provides an opportunity to strengthen institutional capacity, clarify technical standards and establish reliable interoperability before the wider compliance regime takes effect.India has moved from legislating personal data protection towards constructing the institutions needed to implement it. The opening of Consent Manager registration is a substantive development, but its ultimate significance will depend on whether individuals acquire genuine, convenient and enforceable control over their information. The success of the framework will be measured not by the number of intermediaries registered, but by their ability to make privacy rights effective in everyday digital transactions.
