
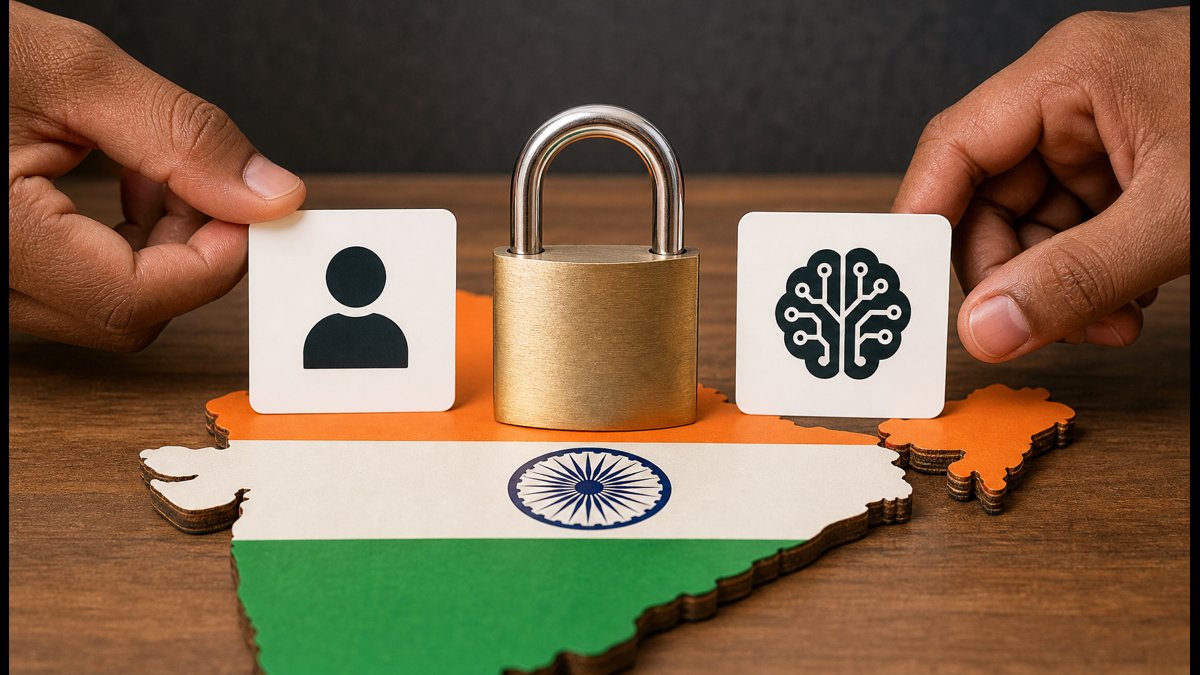
On 31 October in Bengaluru, MeitY unveiled a DEPA-for-AI Training handbook. It proposes purpose-bound, consent-led data pipelines so models train inside secure environments. The release framed it as a techno-legal playbook, not a binding law. Startups and global capability centres are eyeing pilots. Students should track roles in data governance.
A simple idea anchors the framework: the model goes to the data. As Principal Scientific Adviser Ajay Kumar Sood said, “Under DEPA, the model travels to the data, rather than the data travelling to the model.” Training occurs in controlled “sealed-room” environments with provenance trails and safeguards.

How DEPA-for-AI Training consent pipelines and sealed rooms would work
Data providers such as hospitals, banks and public agencies register datasets. Data consumers, including startups, researchers and enterprises, request use-case specific access under electronic contracts. Training runs inside secure environments, with differential privacy. Logs and provenance document usage, improving accountability and audits.
Who can share data and who benefits
Early pilots are expected in finance and healthcare, where data remains locked. Banks and hospitals could share de-identified records under strict terms, while keeping raw data local. Startups and global capability centres can build models for risk, fraud, triage and operations. Researchers gain diversity and scale without breaching confidentiality or licenses.
Compliance stack: DPDP Act, IT Rules and audit logs
The handbook is advisory; existing rules still apply. Align consent, purpose limitation and retention with the Digital Personal Data Protection Act and Information Technology Rules. Maintain dataset inventories, model cards, lineage and training logs. Ensure approvals from your data protection officer before pilots. Provenance features support traceability across workflows.
Next 30–60 days: consultations, pilots and an action checklist
Begin Monday with three actions. Map high-value datasets and identify sensitive fields. Draft a sealed-room pilot with one bank or hospital partner. Stand up access governance, incident playbooks and model-logging. Monitor MeitY channels for consultation updates. For telecom use-cases, note TRAI’s draft responsible-AI guidelines seek comments until 27 November 2026.
Jobs and skills: how students and professionals can prepare
Expect openings for data stewards, privacy engineers, federated-learning specialists and machine-learning security roles. Students can pair Python with data governance, privacy engineering and MLOps courses. Watch for MeitY’s consultation window and sector pilots. Telecom aspirants should diarise the 27 November TRAI deadline, and align projects to responsible-AI compliance needs.
